SOC Analyst Project (SIEM Server (Splunk))
In ProgressDeploying Splunk Enterprise as a homelab SIEM — ingesting endpoint telemetry, building ATT&CK-mapped detections, and practising real SOC analyst triage workflows.
Tech stack:
Elastic
MITRE ATT&CK
Splunk
Suricata
Sysmon
UniFi
Wazuh
Standing up a real Splunk Enterprise SIEM inside my homelab to build hands-on security-operations skills as I move toward a SOC analyst role. Rather than a toy install, the goal is a working detection pipeline I can grow: ingest telemetry from across the lab, write and tune detections, and practise the triage workflow an analyst actually lives in.
What’s built so far
- Splunk Enterprise deployed on a dedicated Ubuntu 24.04 LTS VM in my Proxmox cluster, running as a hardened non-root service and managed by systemd so it survives reboots.
- Placed on a segmented VLAN behind my UniFi firewall, keeping the SIEM isolated from general lab and client traffic.
- Reproducible, parametrised install script (admin seeding, service user, boot-start) so the whole box can be rebuilt from scratch.
- Search head and web console up and healthy, KVStore online, ready for data onboarding.
In progress
- Enabling the forwarder receiver and rolling out Universal Forwarders to Windows and Linux endpoints across the lab.
- Onboarding Sysmon, Windows Event Logs, and Linux auditd/syslog as normalised sources.
- Writing detection searches and mapping alerts to the MITRE ATT&CK framework.
- Fronting the console with Nginx Proxy Manager for TLS and Authentik SSO, so access is gated the same way as the rest of my services.
Where it’s going
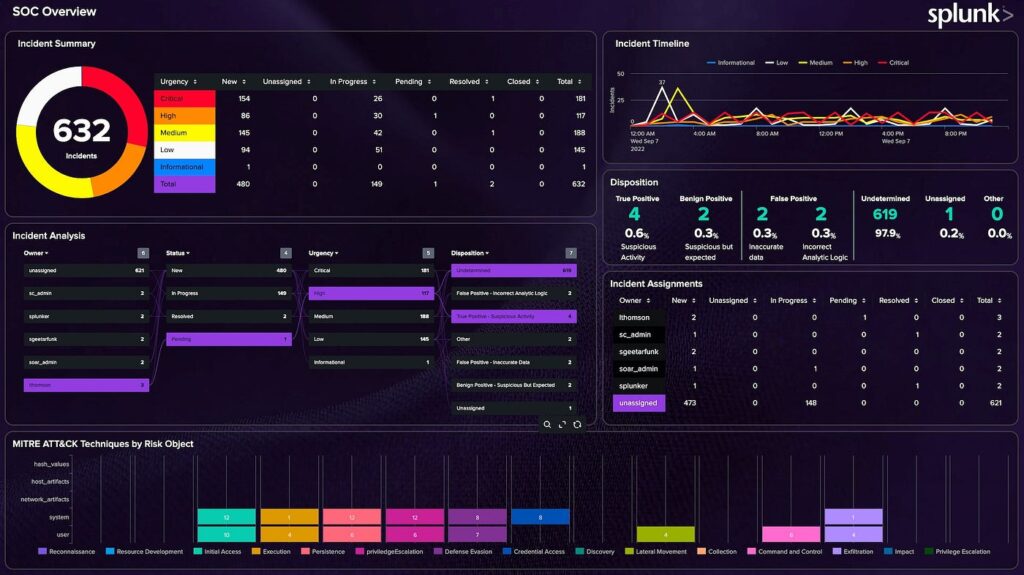
- Building saved searches, alerts and dashboards that mirror a real SOC monitoring workflow.
- Adding Splunk Enterprise Security concepts and layering in threat-intel context.
- Documenting incident triage runbooks I can walk through end to end.
This project ties together the infrastructure side I already run day-to-day with the detection-engineering and analysis skills I’m deliberately building for a security operations career.